We Find Vulnerabilities
Before Hackers Do.
Protect your applications with crowdsourced security.



Crowdsourced Security
Open a channel to the world’s top security researchers. Test your applications and receive only validated, ready-to-fix findings.
350+
Security Researchers
300+
Issues Found
$100k
Paid Rewards
Security Solutions
Offensive security for every stage.
From crowdsourced competitions to dedicated pentests, pick the solution that fits your goals, or combine them in one platform.
Founders
Built by hackers, for security teams.
We spent years on the offensive side. Bypassec is the platform we wished existed when we were the ones finding the bugs.
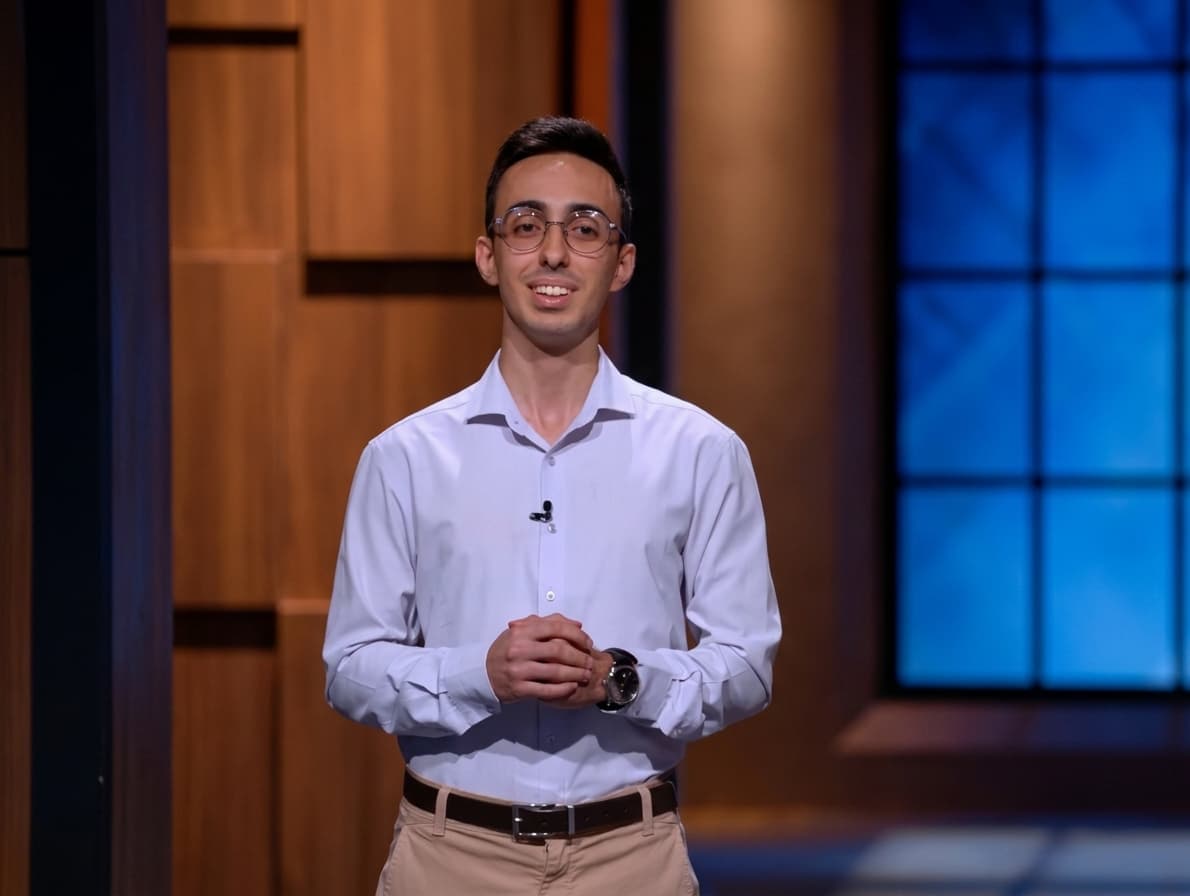
Henrique Scocco
Founder of Bypassec, offensive security and blockchain security researcher with 8 years of experience securing global tech companies, fintechs and Web3 projects, including Uber and OpenZeppelin. OSCP and OSWE certified, Microsoft Hall of Fame awardee and recognized by 30+ companies for critical vulnerabilities.
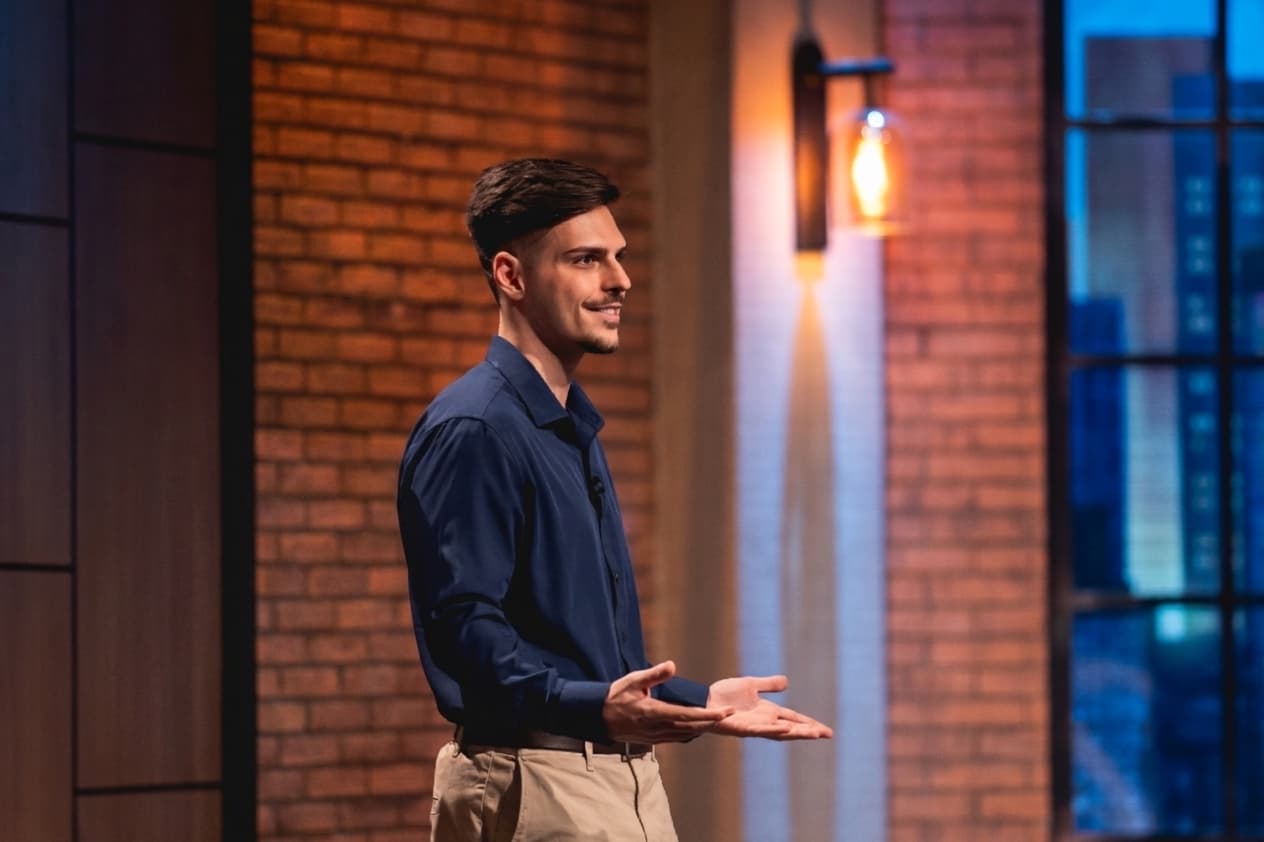
Lucas Bueno
Offensive Security Specialist with 6+ years of experience in cybersecurity, having worked at big tech companies such as Uber and Mercado Libre. Specialized in penetration testing across web applications, APIs, mobile, cloud, and LLMs, holding a degree in Cybersecurity and industry-recognized certifications, including OSWE and eWPTX.
FAQ
Frequently asked questions
It's a collective intelligence channel. We connect companies with security researchers who find and report flaws in their systems in exchange for rewards. This discourages crime and protects organizations before hackers can exploit them.
A pentest gives you one or two testers for a fixed number of hours. A bug bounty is open-ended and often noisy. Competitions combine the best of both: many skilled researchers, a defined scope and timeline, and a predictable budget paid for results.
Our community is made up of experienced web security researchers. Each one goes through identity verification and a skills assessment, and their ranking is based on the quality of past findings. You can also restrict a competition to invite-only researchers.
Your public applications are already being tested by attackers, 24/7. We connect a community of researchers to test them too and report what they find through our channel, which discourages crime. Without a channel, you get hacked. With one, you receive the flaws and stay secure.
You set a reward pool based on your assets and goals. Researchers are paid only for validated vulnerabilities according to severity, so you never pay for hours without results. Unused budget stays with you.
Most competitions go live within a few days. We help you define the scope, invite the right researchers, and you start receiving validated findings from the first day of testing.
$ schedule --call expert
See your app the way an attacker does.
Book a call with one of our security specialists. We'll map your attack surface and help you scope the right competition or pentest.
Book a meeting30-min call · No commitment